Compliance-ready software development for US businesses
Build and scale software for the US market with compliance embedded into the way your product is designed, developed, and released. Modsen brings proven engineering practices, data protection, and delivery discipline to new products and existing teams.
Security-first SDLC
Data protection by design
Human-reviewed AI
Compliance readiness
Engineering for regulated US environments
Value
50% lower data breach risk
15% higher user retention
6 months to achieve the HIPAA compliance goal
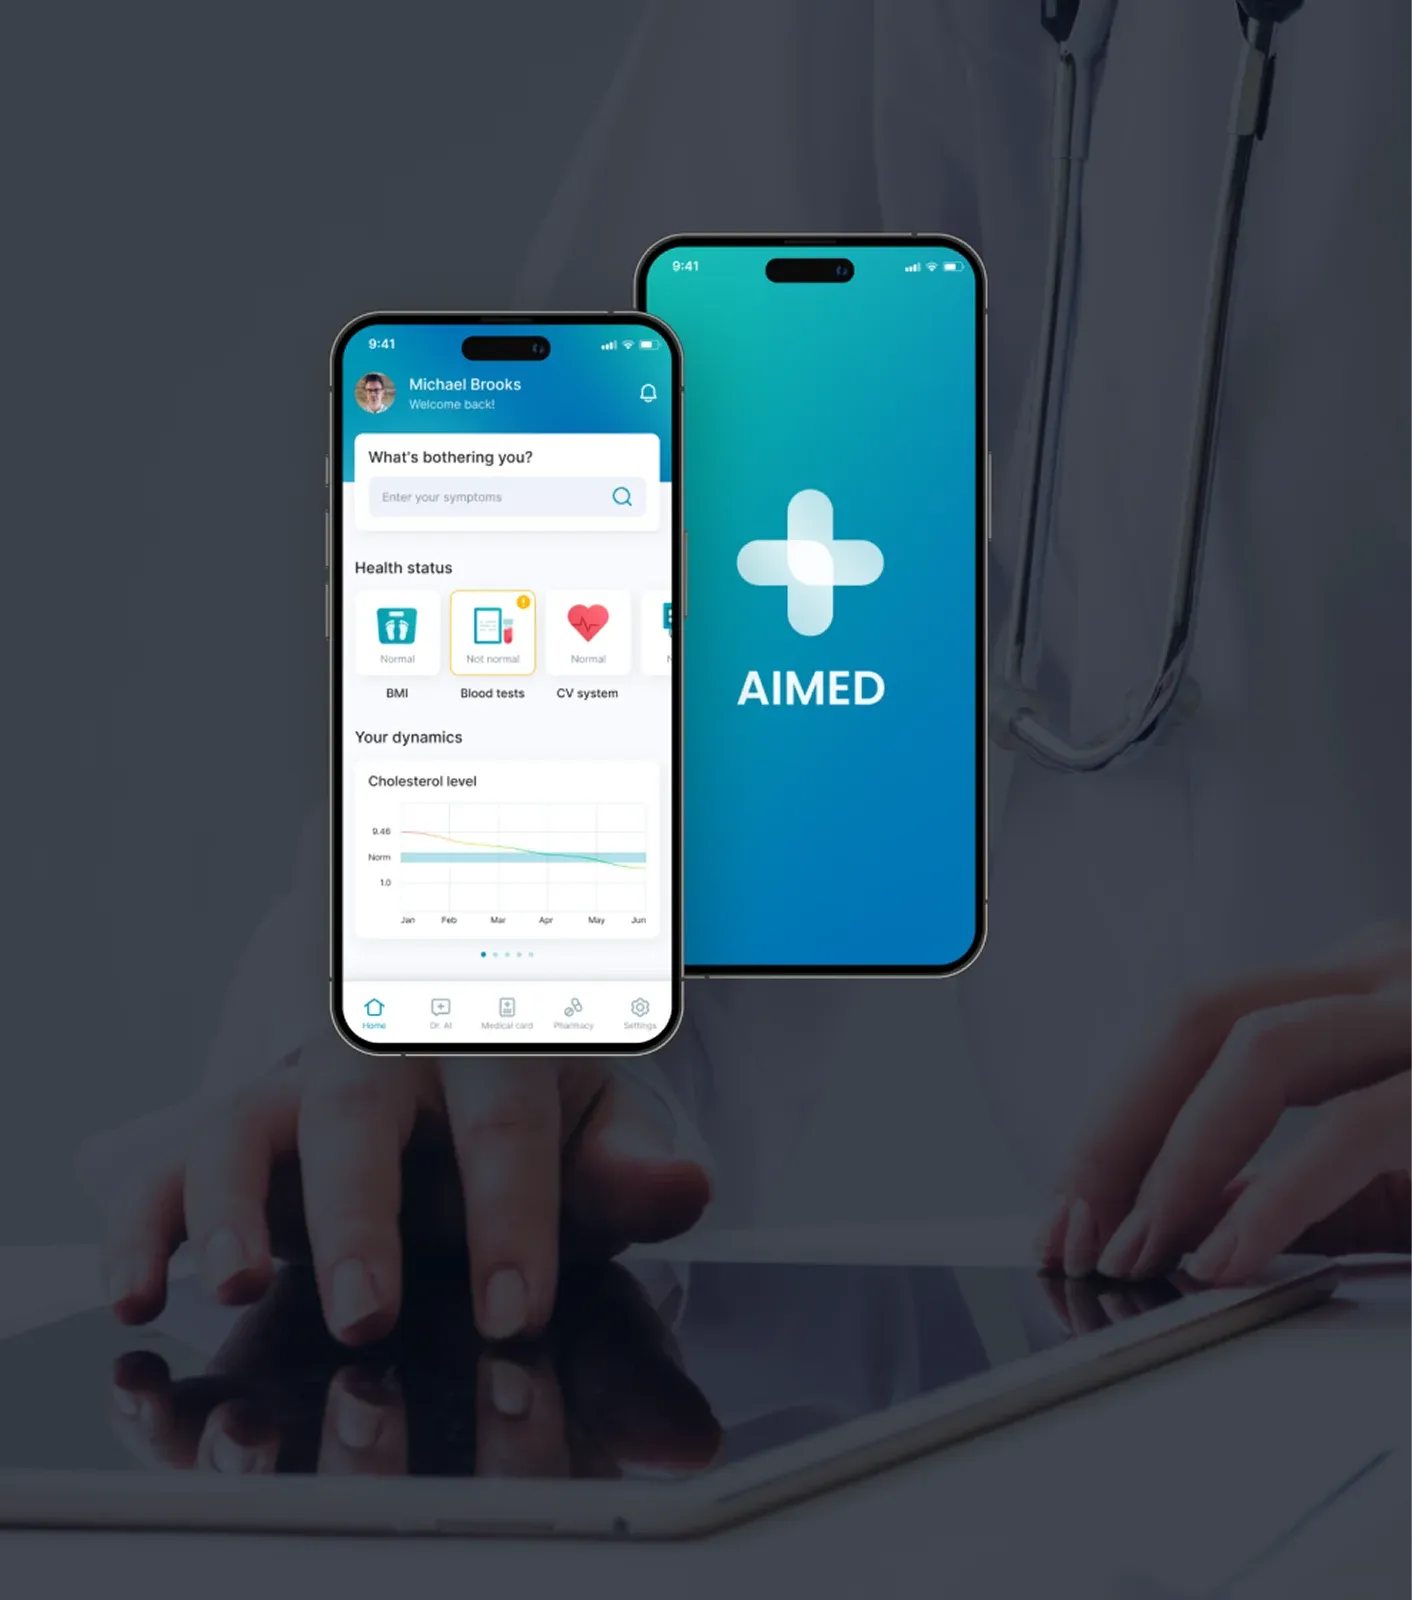
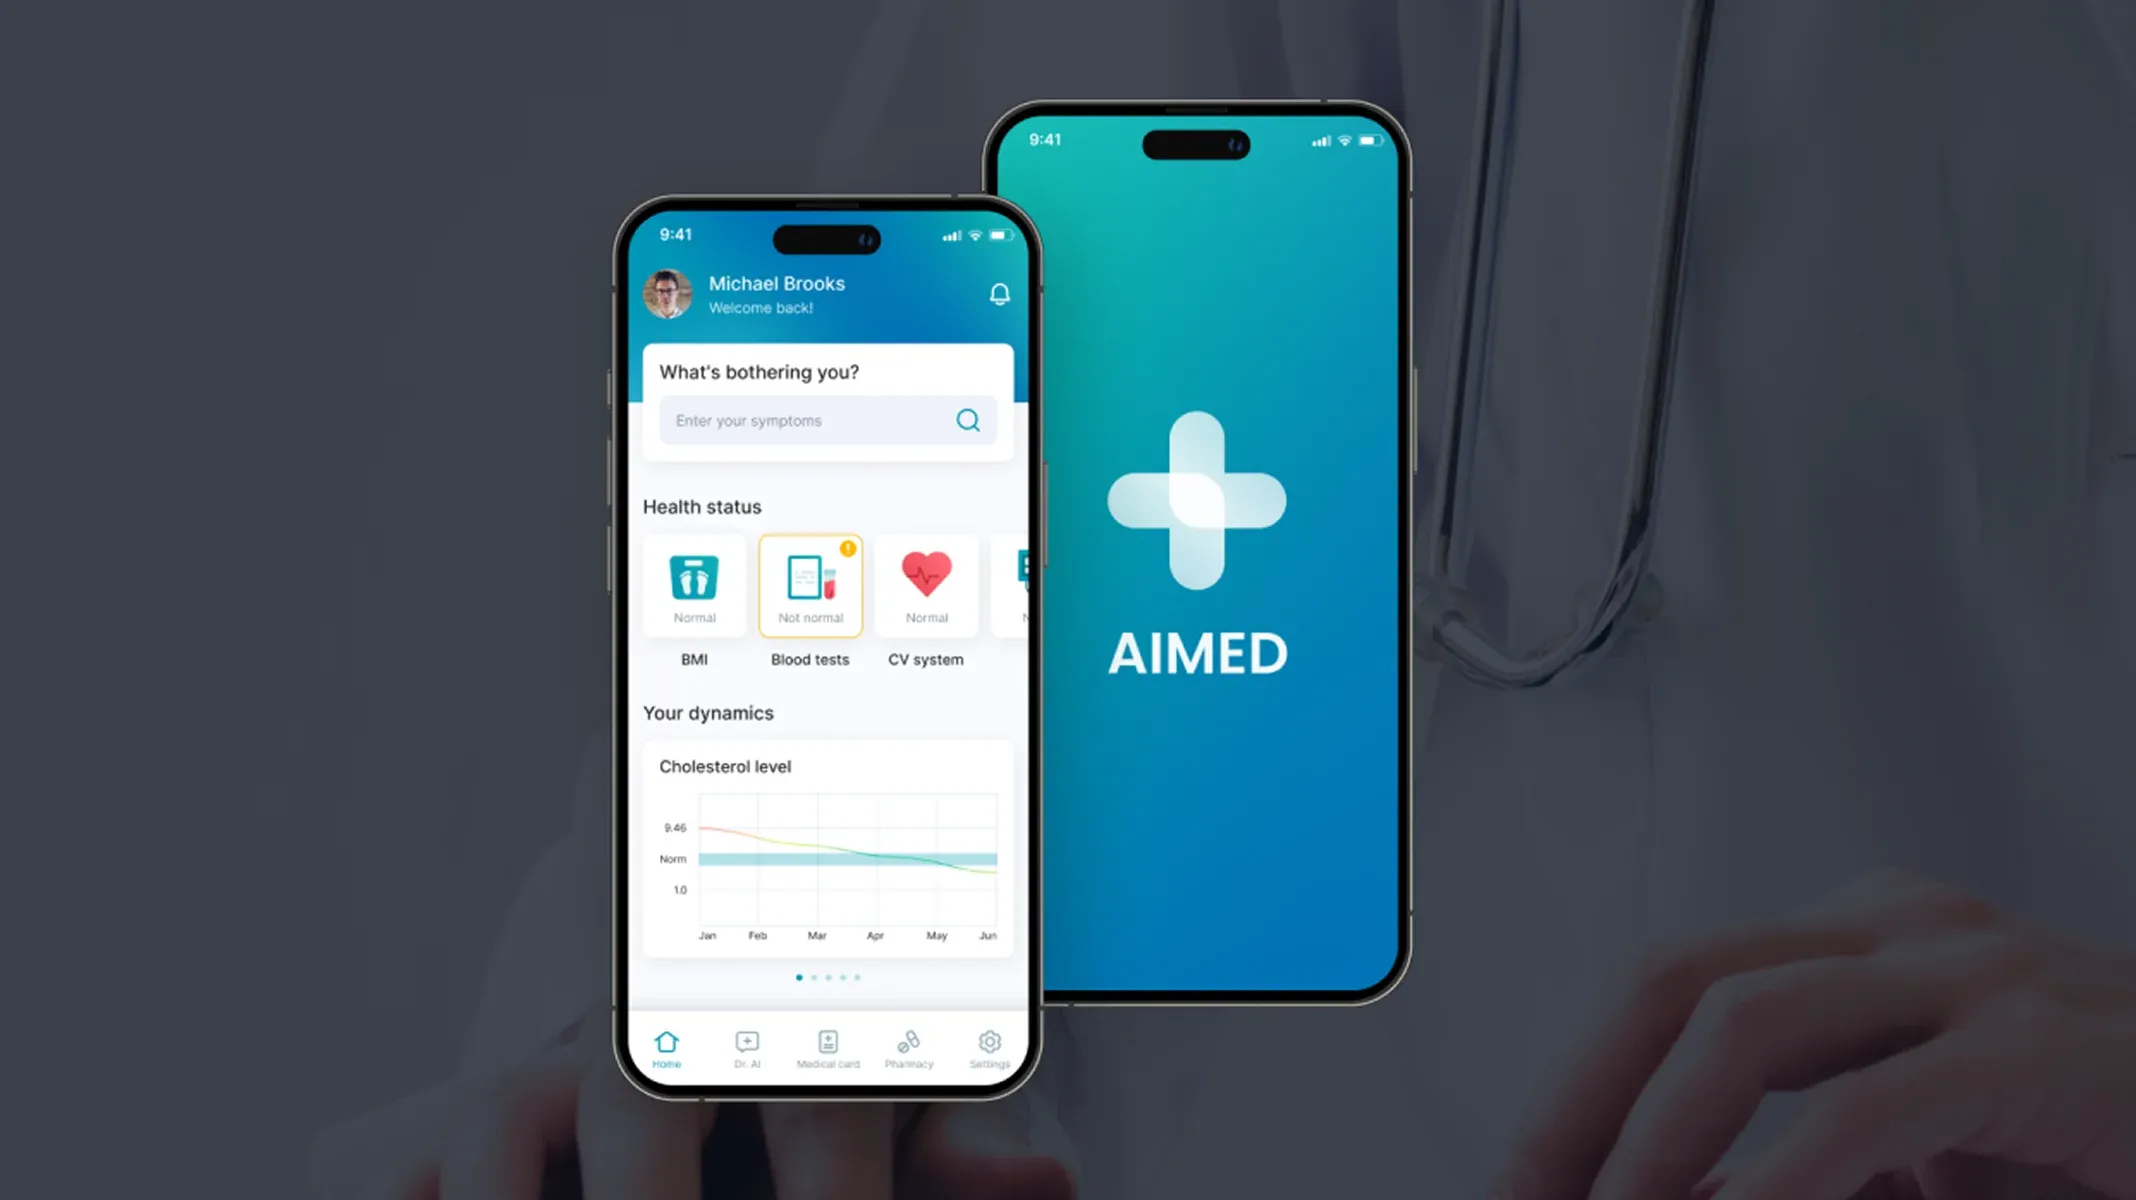
HIPAA compliance audit for a US healthtech platform
AI · 3-week audit · 3 specialists
Challenge
An AI-powered health platform aggregating medical and pharmacy data faced HIPAA compliance gaps around PHI protection and readiness for external assessment.
Solution
Complete HIPAA compliance assessment with identified security gaps and a prioritized remediation roadmap covering encryption, role-based access, monitoring, and privacy-preserving AI.
Value
50% lower data breach risk
15% higher user retention
6 months to achieve the HIPAA compliance goal
Compliance support at every stage of your software journey
Custom software development
We incorporate agreed compliance, security, and data protection requirements across the full development lifecycle – from architecture and data flows to implementation, testing, release, and documentation.
new products
software modernization
regulated workflows
security-sensitive systems
IT consulting
We assess the existing software and engineering environment against defined requirements, identify technical gaps and risks, and turn the findings into a prioritized remediation roadmap your team can act on.
compliance readiness
security assessment
architecture review
remediation planning
Team augmentation
Our engineers join your existing delivery environment and work within your established secure SDLC, access model, coding standards, review procedures, documentation requirements, and release controls.
additional capacity
remediation work
compliance-driven delivery
skill gaps
Trusted expertise across business-critical technologies





How we translate compliance requirements into engineering decisions
Compliance requirements shape architecture, data flows, access controls, integrations, testing, and releases. We bring them into the engineering process early, working with your product, security, legal, and compliance stakeholders to carry agreed requirements from architecture through implementation and release.
Map regulatory requirements to the build
We identify the US regulatory and industry-specific requirements relevant to the project and translate the confirmed scope into architecture, data handling, security controls, and testing criteria.
Bring customer and partner obligations into delivery
Security requirements from enterprise customers, payment providers, partners, and vendors are incorporated into technical scope before they become blockers during procurement, integration, or release.
Fit into your existing security environment
Already have a secure SDLC, access policies, architecture standards, or internal controls? Modsen engineers work within them, keeping delivery aligned with the processes your security and compliance teams already use.
Hands-on experience with US compliance requirements
The requirements affecting US software vary by industry, data type, customer contracts, and operating model. We align engineering practices with the frameworks and controls relevant to each engagement.
Healthcare & health data
HIPAA · HITECH · 42 CFR Part 2 · FTC Health Breach Notification Rule · HITRUST-related requirements
Payments & commerce
PCI DSS requirements · TCPA · CAN-SPAM · payment data security
Privacy & consumer data
CCPA/CPRA · US state privacy laws · COPPA · FTC privacy & security requirements · GDPR where applicable
Enterprise security
SOC 2-oriented environments · NIST CSF · customer security policies · vendor security requirements
Financial services & fintech
GLBA · FTC Safeguards Rule · financial data security requirements · SEC cybersecurity requirements where applicable
Accessibility & regulated records
ADA · WCAG-oriented accessibility requirements
Education & student data
FERPA · student data privacy requirements
Regulated digital records
21 CFR Part 11 · electronic records · electronic signatures

Start your next US project with compliance in scope
Whether you need a new software product, a review of your current environment, or engineers who can work within your existing controls, our team can define the right starting point.
Compliance built into every stage of delivery
Discovery & requirement mapping
We map the US regulatory, security, and project-specific requirements that need to shape delivery.
Architecture & data design
Requirements inform data flows, encryption, access controls, integrations, logging, infrastructure, and architecture.
Development
Engineers follow agreed secure coding, data-handling, access, dependency, and secrets management practices.
Code review & security checks
Code reviews and automated checks help identify vulnerabilities, unsafe dependencies, exposed secrets, and other risks.
QA & validation
We test functional scenarios alongside applicable security, privacy, access, and data-handling requirements.
Release & documentation
Release controls and technical documentation maintain traceability from requirements through testing and production.
Maintenance & change control
New features, integrations, dependencies, and infrastructure changes are reviewed against established requirements.
AI use aligned with your security environment
AI doesn't have to be used the same way on every project. We adapt its role in the engineering workflow to your US regulatory environment, security policies, data restrictions, and internal AI governance.
No-AI delivery
Restricted environments Sensitive IP Client-mandated AI restrictions
Controlled AI use
Enterprise software Regulated products Established security policies
AI-augmented delivery
Faster release cycles Routine development at scale Expanded QA coverage
Your compliance framework. Our engineering responsibility
We support compliance through engineering. Certification and legal compliance remain with the responsible organization and, where applicable, accredited assessors.
Your team
Defines applicable legal and organizational obligations Approves policies and risk decisions Owns certification and organizational compliance
Modsen
Translates agreed obligations into technical requirements Implements engineering and security controls Tests agreed scenarios Maintains technical documentation and evidence Works with your security/compliance stakeholders
Why US businesses trust Modsen with their software
“What impressed us most was the combination of exceptional technical expertise and an outstanding work ethic.”
CTO · Enterprise
U.S. bank · US
Clutch · Verified

“Their strong eCommerce expertise and architectural approach helped us make well-considered technical decisions and bring new AI features to market quickly.”
Ethan Calloway, CTO · Retail & eCommerce
Oakridge · US
TechBehemoths · Verified
“They are just so reliable. We have asked them for some hard technical input and they always rise to it.”
Executive · Software & Globalization
Lingoport Inc · US (Colorado)
Clutch · Verified
Make compliance work for your engineering economics
Protect engineering investment
Bringing requirements into architecture and development early reduces the risk of expensive rework when the product is already close to release.
Reach the US market with fewer roadblocks
Regulatory, security, and data requirements are addressed within delivery rather than becoming a separate hurdle before launch.
Remove barriers to enterprise deals
We keep security controls and technical evidence in scope throughout delivery, helping your product meet technical expectations during enterprise procurement and security reviews.
Make AI productivity usable
Modsen applies AI within approved boundaries, so development and QA can move faster without stepping outside established data and security policies.
Keep delivery predictable
Requirements remain connected to implementation, testing, and release, giving product teams better visibility into scope and dependencies.
FAQ – US software compliance & security
Can Modsen work within our existing secure SDLC?
Which US compliance frameworks does Modsen have experience working with?
Can you help if we already have a product with compliance or security gaps?
How do you handle access to sensitive data and production environments?
How do you use AI tools on security-sensitive projects?
What documentation can you provide for security and compliance reviews?
Build once. Scale across the US with compliance in scope